



One-Time Password (OTP)
What is One-Time Password (OTP)?
A one-time password (OTP) is a randomly generated code valid for a single authentication session or transaction, used as a second factor to verify a user’s identity.
A one-time password (OTP) is a single-use verification code — typically 4 to 8 digits — generated by a server and delivered to a user through SMS, email, WhatsApp, Telegram, or voice call. The code expires after a short window, usually 60 to 120 seconds, and cannot be reused. OTPs serve as the second factor in two-factor authentication (2FA), adding a possession-based check (the user’s phone) to a knowledge-based check (the user’s password). Businesses use OTPs for login verification, transaction confirmation, password resets, and account registration. The delivery channel matters: SMS OTP reaches any phone without internet, while app-based OTP (Telegram, WhatsApp) requires the user to have the app installed. Production OTP systems typically use cascade routing — trying the cheapest channel first and falling back to SMS if delivery is not confirmed — to balance cost and reliability. BSG’s 2FA solution supports OTP delivery across SMS, Telegram, WhatsApp, and voice with automatic failover.
BSG covers this in more depth in How Can You Use OTP via SMS to Improve Customer Service & Privacy?.
Related terms
Related BSG products
Зацікавлені у спеціальній пропозиції?
Готові розширювати можливості?
Давайте обговоримо.


Схожі терміни
Рішення BSG
Корисні Матеріали
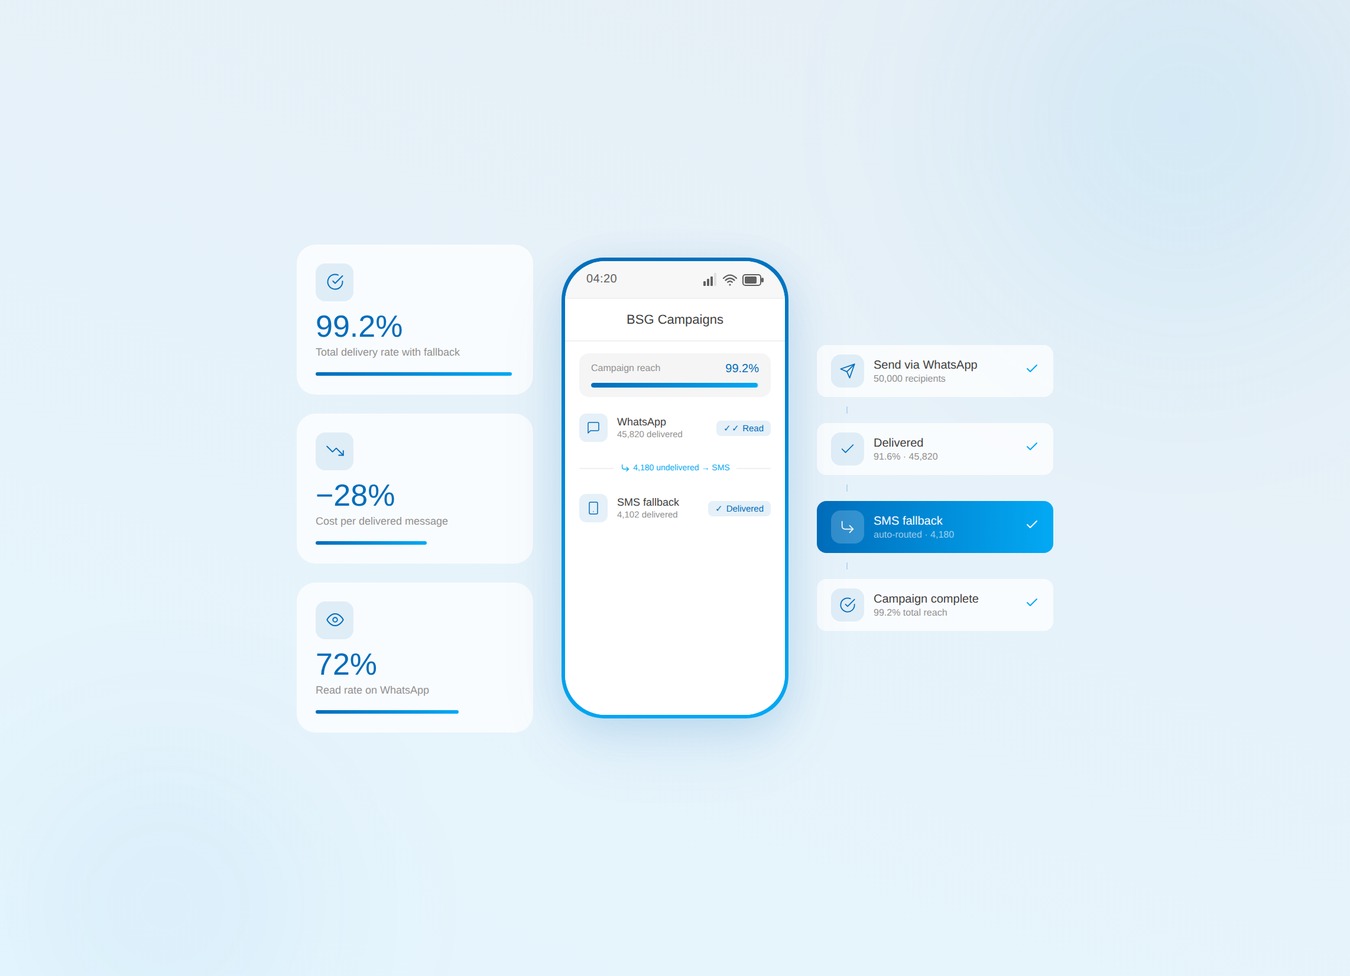
Bulk SMS alone leaks budget. Verify the list, then run WhatsApp-first with SMS fallback.
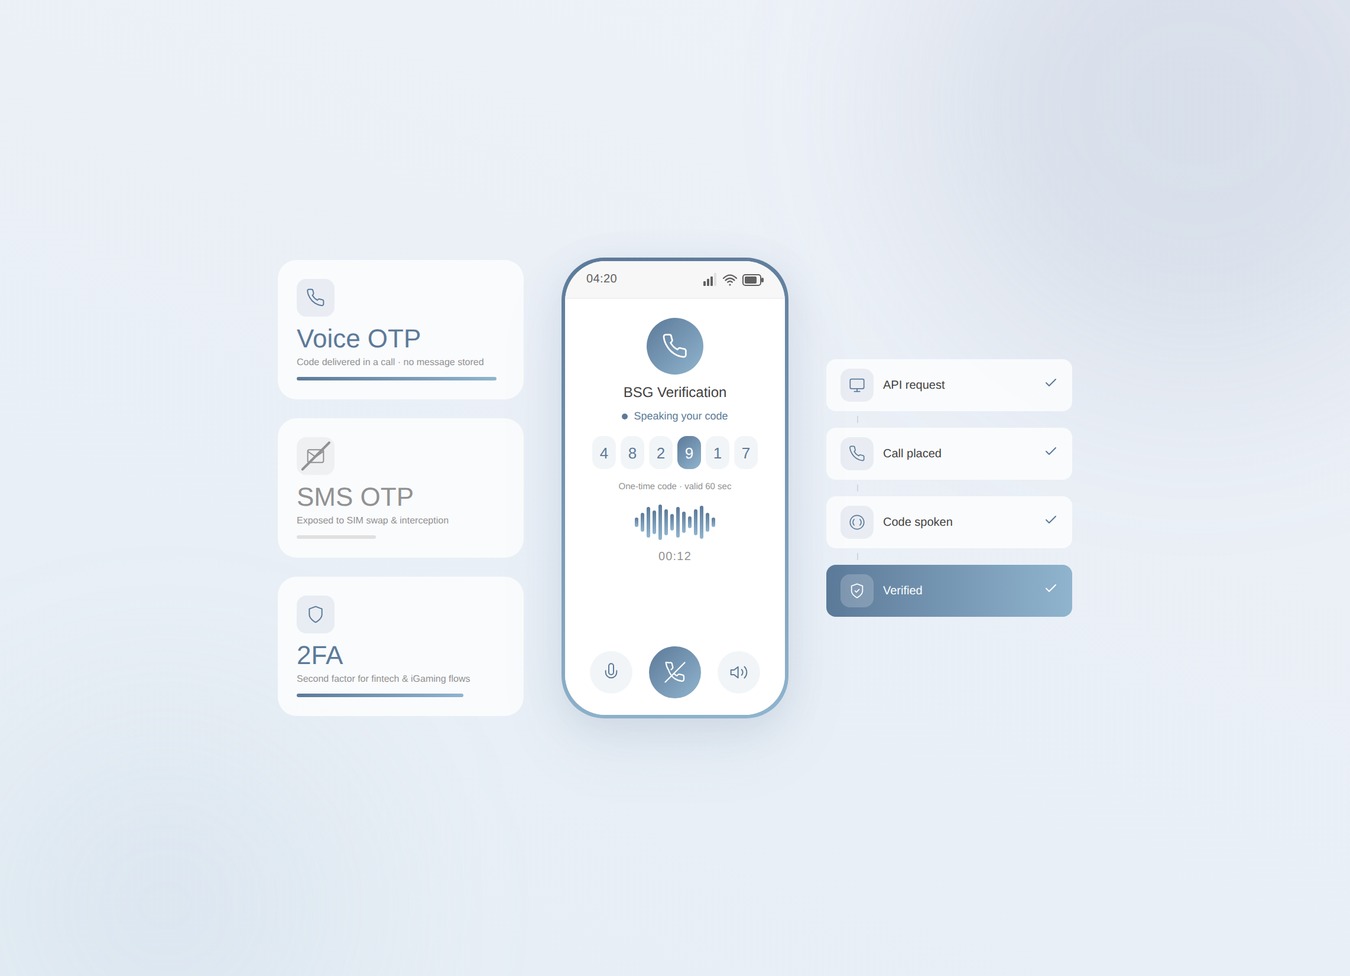
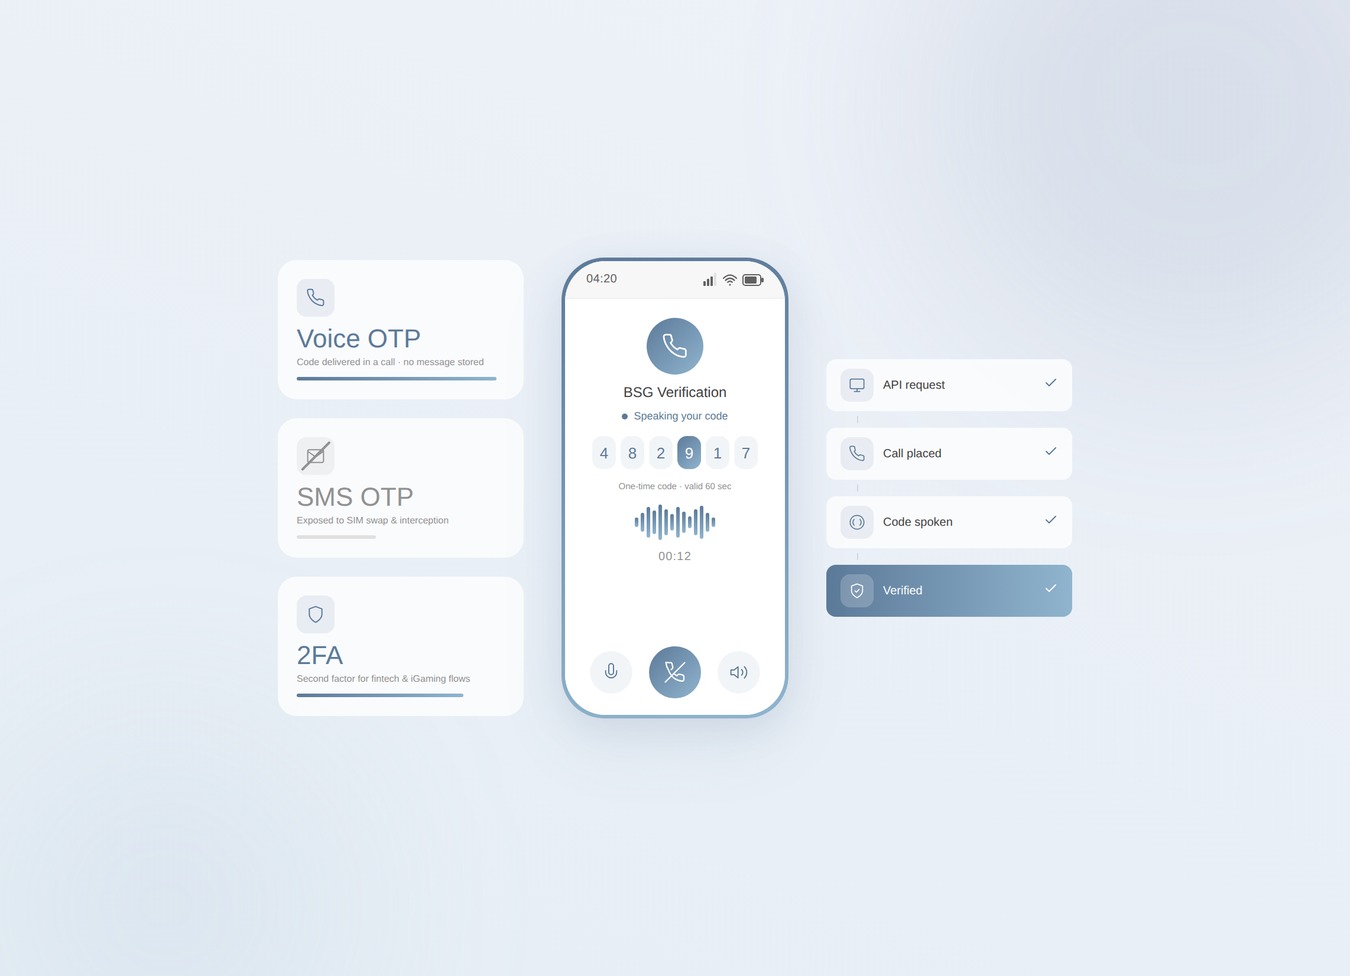
SIM swaps jumped 1,055% in a year. Voice OTP takes your riskiest codes off the SMS rail.
Telegram OTP is free — until it silently fails. Know the limits and when to add fallback.