



HOTP (HMAC-Based One-Time Password)
What is HOTP?
HOTP (HMAC-Based One-Time Password) is a one-time verification code generated using a shared secret key and an incrementing counter, where each new code is triggered by a successful authentication event rather than a time interval. Platforms like BSG's 2FA/OTP Platform deliver such codes over SMS, voice, or messaging apps.
For more on this, see BSG's 2FA, TOPT, Push-Based Authentication: Comparison.
How does HOTP work?
HOTP generates codes using HMAC-SHA1 — a hash function that combines a shared secret with a counter value. Every time the user successfully authenticates, the counter increments on both the client device and the server. The next login attempt produces a different code based on the updated counter.
How does HOTP differ from TOTP?
The key difference from TOTP is persistence: an HOTP code does not expire after 30 seconds. It remains valid until the user authenticates again or the server advances the counter. This makes HOTP practical for hardware tokens (like YubiKey in HOTP mode) where users may generate a code and enter it minutes later.
When is HOTP still used?
The downside of HOTP is a wider attack window. A stolen HOTP code can be used at any point before the next legitimate login — unlike TOTP, where the window closes in 30 seconds regardless. For this reason, most modern consumer-facing platforms prefer TOTP or SMS OTP over HOTP. HOTP remains common in enterprise hardware token deployments and legacy systems where time synchronization between server and device is unreliable. The RFC 4226 standard defines the HOTP algorithm.
Interested in a special offer?
Ready to reach further?
Let’s talk


Related Terms
Explore BSG Solutions
Useful Materials
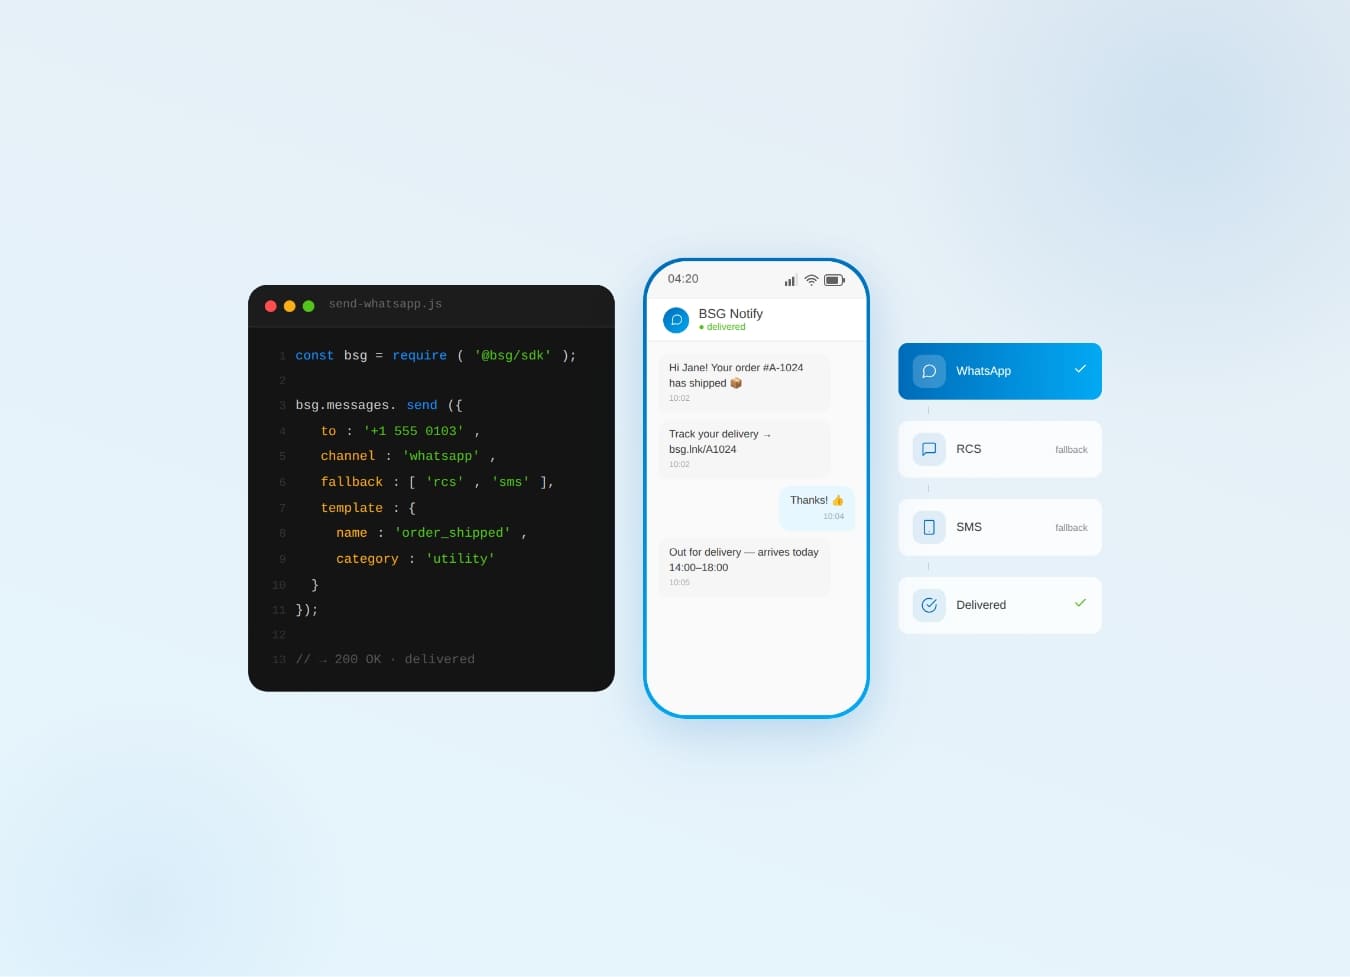
WhatsApp Business API for 2026 — setup steps, the new per-message pricing model, and proven use cases by industry.
What is CPaaS? The cloud API layer that adds SMS, WhatsApp, voice & OTP to your apps — how it works and why it beats a multi-vendor stack.
Why one communication API for SMS, WhatsApp, Viber & RCS beats five separate integrations — cascade fallback, unified reports.